Cyber intelligence with context
Connect public and authorised sources, threat signals, techniques and assets within scope. Distinguish a contextual signal from a supported finding.
Cyber intelligence that connects technical findings to what matters to your business.
Connect exposure, threats and business risk in one decision process. Keep the evidence behind each finding and turn analysis into priorities, recommendations and reports you can act on.
For security, risk and leadership teams.
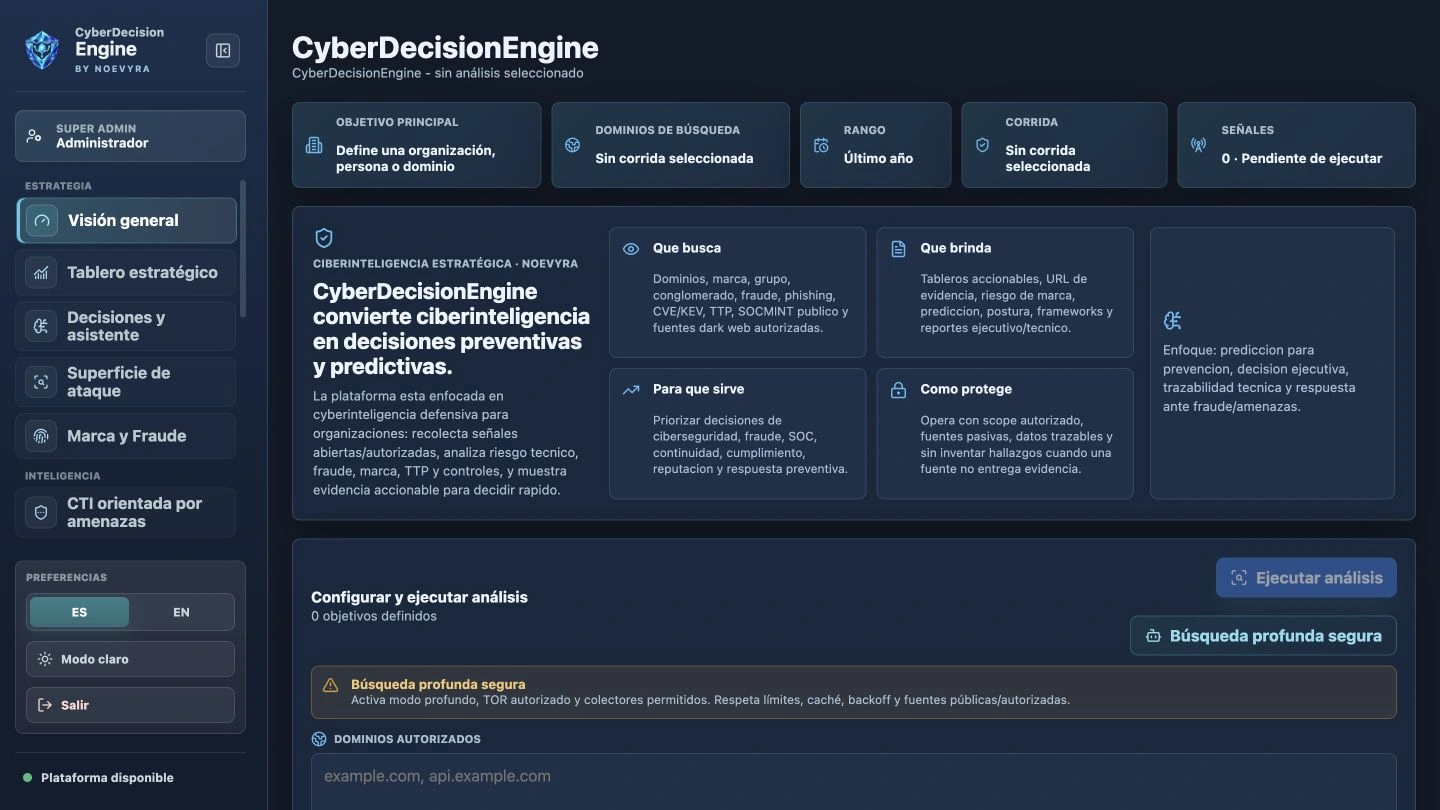
Focus review on what matters to your organisation.
Preserve the link between evidence, interpretation and action.
Connect the analyst’s conversation with leadership’s.
CAPABILITIES
Intelligence, risk and traceability together: see what is exposed, why it matters and which action takes priority.
Connect public and authorised sources, threat signals, techniques and assets within scope. Distinguish a contextual signal from a supported finding.
Separate severity, plausibility, impact, confidence and controls. Review inherent and residual risk alongside evidence and limitations.
Explore external attack surface, brand, fraud, disinformation and AI security; classify evidence across IT, IoT, IIoT and OT when supported.
Connect findings, scenarios and recommendations. Bring the same context to dashboards, executive and technical reports, and JSON/CSV exports.
Access is organised by role and organisational permissions. Set up MFA with an authenticator app using a QR code or manual key.
INSIDE THE PLATFORM
Explore the platform: from the origin of each piece of evidence to its relationship with threats, controls and business decisions. Enlarge the views to see the workflow.
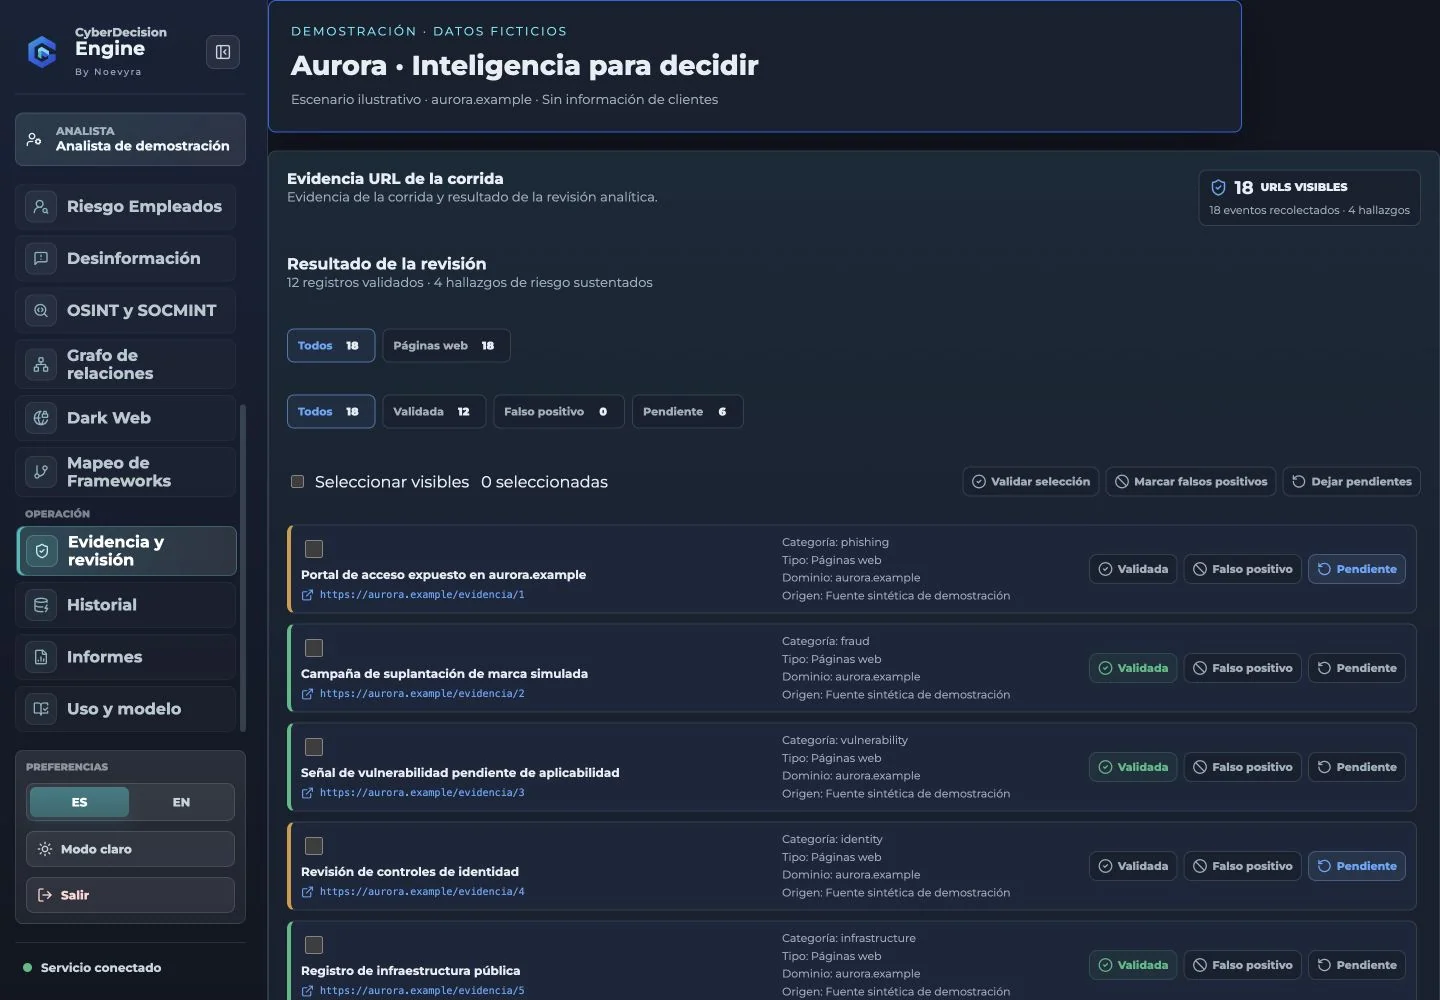
Review origin, status and relationship to the scope. Information retains its context for analyst review.
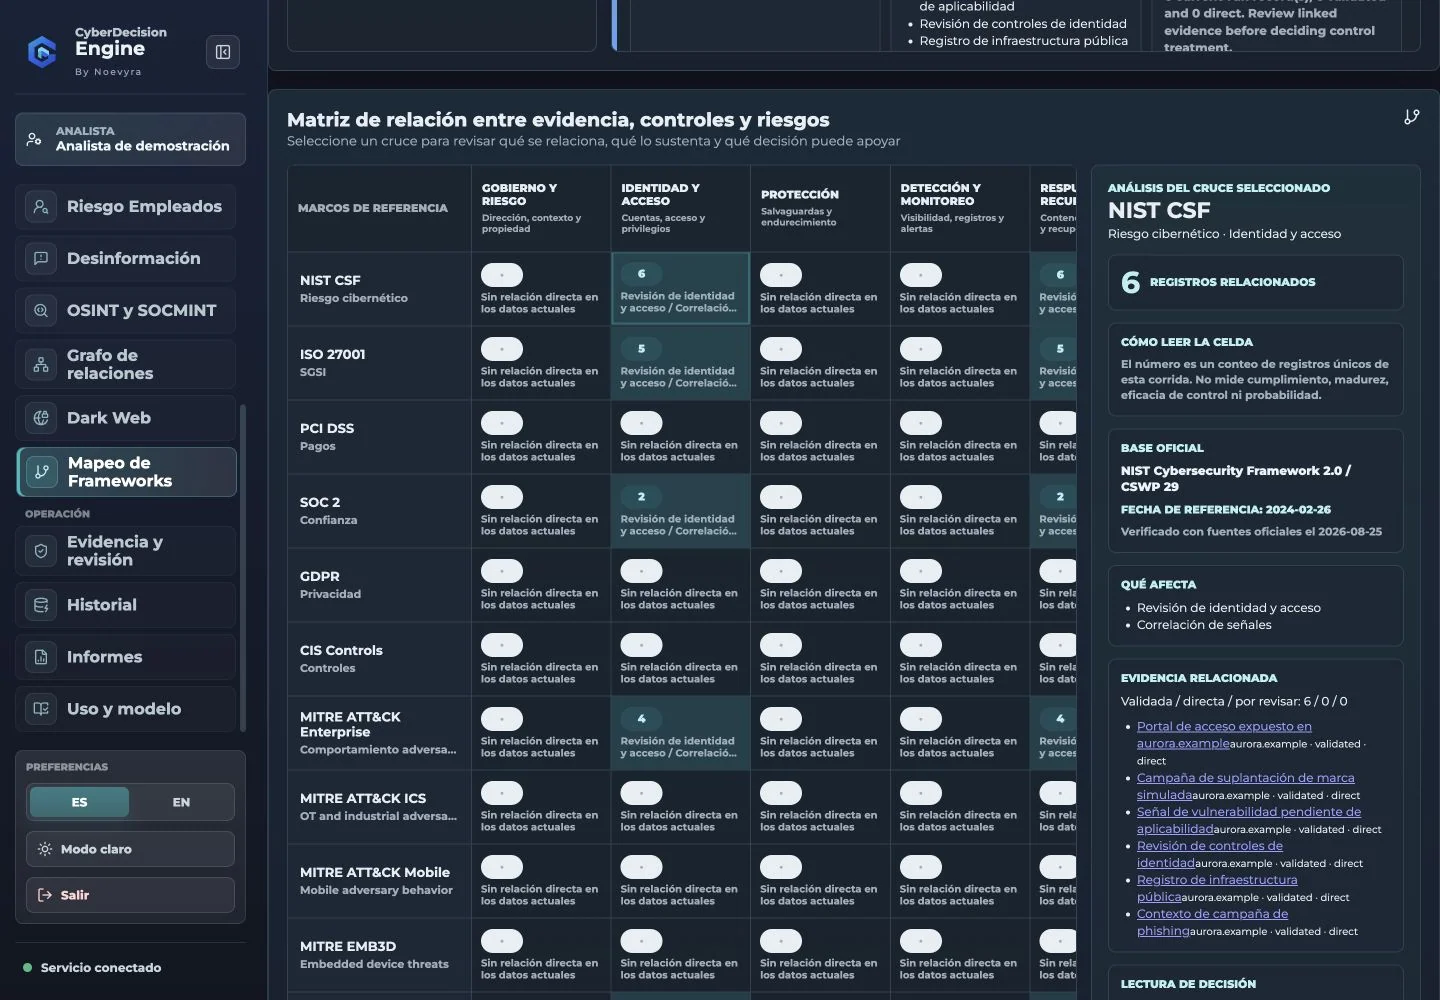
Connect evidence with techniques, controls and risk areas. Mapping helps guide review; it does not amount to certification.
P-CIDER METHOD
CyberDecisionEngine implements P-CIDER, NOEVYRA’s method for connecting cyber intelligence, evidence and business risk to support strategic decisions.
Claim → Evidence → Interpretation → Limitation → Decision → Closure
Define the organisation, scope and authorisation.
Consult sources and preserve their limitations.
Connect and review the evidence.
Support the relevant scenarios.
Assess impact, confidence and risk.
Guide actions and review their completion.
REFERENCES THAT CONNECT DISCIPLINES
Frameworks are used as analytical references according to the available evidence. Their inclusion does not imply endorsement, certification or automatic compliance.
FOR YOUR ORGANISATION
Connect signals, techniques and public attack surface to guide investigation and response.
Review scenarios, controls and priorities with visible evidence and limitations.
Understand exposure, implications and proposed actions through executive reports.
BUSINESS DEMO
Request a demonstration to explore the platform with your team. If you already know the product, you can also ask directly about licences and pricing for your organisation.
Submitting a request does not create an account or make a purchase.
Ask about licences and pricing ↗
Already have access? Sign in to the platform ↗It connects technical findings with threats, controls, scenarios and business impact. Its difference is full decision traceability and the use of P-CIDER to turn evidence into priorities that security, risk and leadership can review.
Public and authorised sources within an agreed scope. Availability depends on configuration, integrations and permissions. Each analysis preserves the limitations of its sources.
No. Signal-pressure indices are not calibrated probabilities of attack. Framework mappings guide analysis and do not represent certification or guarantee compliance.
You can request a demo or ask directly about licences and pricing by email. The NOEVYRA team will learn about your organisation’s scope and guide you through the business options.